

An growing variety of proposed purposes on high of Ethereum depend on some sort of incentivized, multi-party knowledge provision – whether or not voting, random quantity assortment, or different use instances the place getting info from a number of events to extend decentralization is extremely fascinating, but additionally the place there’s a robust threat of collusion. A RANDAO can definitely present random numbers with a lot increased cryptoeconomic safety than easy block hashes – and definitely higher than deterministic algorithms with publicly knowable seeds, however it isn’t infinitely collusion-proof: if 100% of individuals in a RANDAO collude with one another, they’ll set the end result to no matter they need. A way more controversial instance is the prediction market Augur, the place decentralized occasion reporting depends on a extremely superior model of a Schelling scheme, the place everybody votes on the end result and everybody within the majority will get rewarded. The idea is that when you count on everybody else to be sincere, your incentive can also be to be sincere to be within the majority, and so honesty is a secure equilibrium; the issue is, nonetheless, that’s greater than 50% of the individuals collude, the system breaks.
The truth that Augur has an impartial token supplies a partial protection in opposition to this drawback: if the voters collude, then the worth of Augur’s token may be anticipated to lower to near-zero because the system turns into perceived as ineffective and unreliable, and so the colluders lose a considerable amount of worth. Nonetheless, it’s definitely not a complete protection. Paul Sztorc’s Truthcoin (and likewise Augur) features a additional protection, which is kind of economically intelligent. The core mechanism is easy: reasonably than merely awarding a static quantity to everybody within the majority, the quantity awarded relies on the extent of disagreement among the many closing votes, and the extra disagreement there’s the extra majority voters get, and minority voters get an equally great amount taken out of their safety deposit.
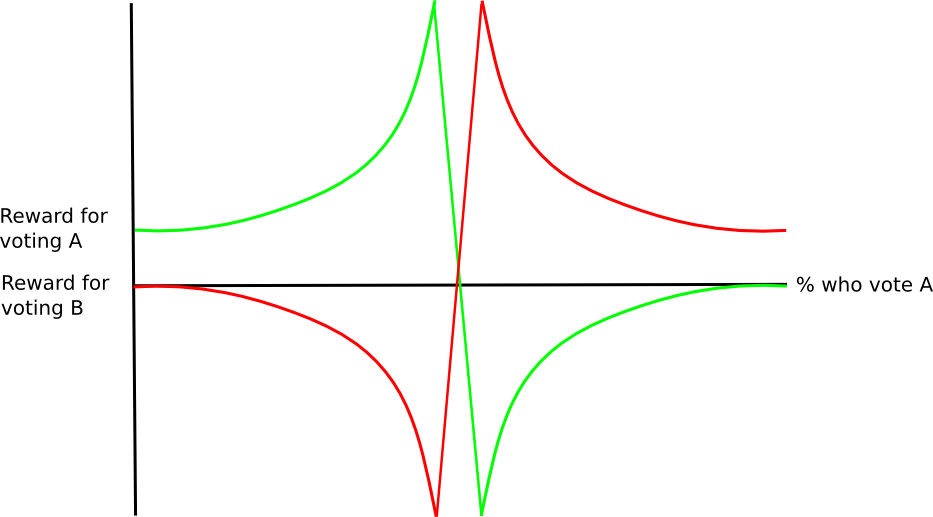
The intent is easy: when you get a message from somebody saying “hey, I’m beginning a collusion; regardless that the precise reply is A, let’s all vote B”, in a less complicated scheme you might be inclined to go alongside. In Sztorc’s scheme, nonetheless, you might properly come to the conclusion that this particular person is really going to vote A, and is attempting to persuade only some p.c of individuals to vote B, in order to steal a few of their cash. Therefore, it creates a scarcity of belief, making collusions tougher. Nonetheless, there’s a drawback: exactly as a result of blockchains are such glorious units for cryptographically safe agreements and coordination, it’s totally arduous to make it inconceivable to collude provably.
To see how, contemplate the best potential scheme for a way reporting votes in Augur may work: there’s a interval throughout which everybody can ship a transaction supplying their vote, and on the finish the algorithm calculates the end result. Nonetheless, this method is fatally flawed: it creates an incentive for individuals to attend so long as potential to see what all the opposite gamers’ solutions are earlier than answering themselves. Taking this to its pure equilibrium, we’d have everybody voting within the final potential block, resulting in the miner of the final block basically controlling every thing. A scheme the place the top comes randomly (eg. the primary block that passes 100x the same old problem threshold) mitigates this considerably, however nonetheless leaves a large amount of energy within the palms of particular person miners.
The usual cryptographer’s response to this drawback is the hash-commit-reveal scheme: each participant P[i] determines their response R[i], and there’s a interval throughout which everybody should submit h(R[i]) the place h may be any pre-specified hash operate (eg. SHA3). After that, everybody should submit R[i], and the values are checked in opposition to the beforehand supplied hashes. For 2-player rock paper scissors, or another sport which is solely zero-sum, this works nice. For Augur, nonetheless, it nonetheless leaves open the chance for credible collusion: customers can voluntarily reveal R[i] earlier than the actual fact, and others can test that this certainly matches the hash values that they supplied to the chain. Permitting customers to alter their hashes earlier than the hash submitting interval runs out does nothing; customers can all the time lock up a big amount of cash in a specifically crafted contract that solely releases it if nobody supplies a Merkle tree proof to the contract, culminating with a earlier blockhash, displaying that the vote was modified, thereby committing to not change their vote.
A New Answer?
Nonetheless, there’s additionally one other path to fixing this drawback, one which has not but been adequately explored. The thought is that this: as a substitute of creating pre-revelation for collusion functions expensive inside the major sport itself, we introduce a parallel sport (albeit a compulsory one, backed by the oracle individuals’ safety deposits) the place anybody who pre-reveals any details about their vote to anybody else opens themselves as much as the chance of being (probabilistically) betrayed, with none solution to show that it was that particular one that betrayed them.
The sport, in its most elementary kind, works as follows. Suppose that there’s a decentralized random quantity era scheme the place customers should all flip a coin and provide both 0 or 1 as inputs. Now, suppose that we wish to disincentivize collusion. What we do is easy: we permit anybody to register a guess in opposition to any participant within the system (be aware using “anybody” and “any participant”; non-players can be a part of so long as they provide the safety deposit), basically stating “I’m assured that this individual will vote X with greater than 1/2 likelihood”, the place X may be 0 or 1. The principles of the guess are merely that if the goal provides X as their enter then N cash are transferred from them to the bettor, and if the goal provides the opposite worth then N cash are transferred from the bettor to the goal. Bets may be made in an intermediate part between dedication and revelation.
Probabilistically talking, any provision of knowledge to another social gathering is now doubtlessly extraordinarily expensive; even when you persuade another person that you’ll vote 1 with 51% likelihood, they’ll nonetheless take cash from you probabilistically, and they’re going to win out in the long term as such a scheme will get repeated. Be aware that the opposite social gathering can guess anonymously, and so can all the time faux that it was a passerby gambler making the bets, and never them. To boost the scheme additional, we are able to say that you simply should guess in opposition to N completely different gamers on the similar time, and the gamers should be pseudorandomly chosen from a seed; if you wish to goal a particular participant, you are able to do so by attempting completely different seeds till you get your required goal alongside a couple of others, however there’ll all the time be not less than some believable deniability. One other potential enhancement, although one which has its prices, is to require gamers to solely register their bets between dedication and revelation, solely revealing and executing the bets lengthy after many rounds of the sport have taken place (we assume that there’s a lengthy interval earlier than safety deposits may be taken out for this to work).
Now, how will we convert this into the oracle state of affairs? Contemplate as soon as once more the easy binary case: customers report both A or B, and a few portion P, unknown earlier than the top of the method, will report A and the remaining 1-P will report B. Right here, we modify the scheme considerably: the bets now say “I’m assured that this individual will vote X with greater than P likelihood”. Be aware that the language of the guess shouldn’t be taken to suggest information of P; reasonably, it implies an opinion that, regardless of the likelihood a random consumer will vote X is, the one explicit consumer that the bettor is concentrating on will vote X with increased likelihood than that. The principles of the guess, processed after the voting part, are that if the goal votes X then N * (1 – P) cash are transferred from the goal to the bettor, and in any other case N * P cash are transferred from the bettor to the goal.
Be aware that, within the regular case, revenue right here is much more assured than it’s within the binary RANDAO instance above: more often than not, if A is the reality, everybody votes for A, so the bets could be very low-risk revenue grabs even when complicated zero-knowledge-proof protocols have been used to solely give probabilistic assurance that they’ll vote for a selected worth.
Aspect technical be aware: if there are solely two prospects, then why cannot you identify R[i] from h(R[i]) simply by attempting each choices? The reply is that customers are literally publishing h(R[i], n) and (R[i], n) for some massive random nonce n that can get discarded, so there’s an excessive amount of house to enumerate.
As one other level, be aware that this scheme is in a way a superset of Paul Sztorc’s counter-coordination scheme described above: if somebody convinces another person to falsely vote B when the actual reply is A, then they’ll guess in opposition to them with this info secretly. Significantly, cashing in on others’ ethical turpitude would now be not a public good, however reasonably a personal good: an attacker that tips another person right into a false collusion may acquire 100% of the revenue, so there could be much more suspicion to hitch a collusion that is not cryptographically provable.
Now, how does this work within the linear case? Suppose that customers are voting on the BTC/USD value, so they should provide not a selection between A and B, however reasonably a scalar worth. The lazy resolution is just to use the binary method in parallel to each binary digit of the value; an alternate resolution, nonetheless, is vary betting. Customers could make bets of the shape “I’m assured that this individual will vote between X and Y with increased likelihood than the common individual”; on this means, revealing even roughly what worth you’re going to be voting to anybody else is more likely to be expensive.
Issues
What are the weaknesses of the scheme? Maybe the most important one is that it opens up a possibility to “second-order grief” different gamers: though one can’t, in expectation, power different gamers to lose cash to this scheme, one can definitely expose them to threat by betting in opposition to them. Therefore, it could open up alternatives for blackmail: “do what I need or I will power you to gamble with me”. That stated, this assault does come at the price of the attacker themselves being subjected to threat.
The best solution to mitigate that is to restrict the quantity that may be gambled, and even perhaps restrict it in proportion to how a lot is guess. That’s, if P = 0.1, permit bets as much as $1 saying “I’m assured that this individual will vote X with greater than 0.11 likelihood”, bets as much as $2 saying “I’m assured that this individual will vote X with greater than 0.12 likelihood”, and many others (mathematically superior customers might be aware that units like logarithmic market scoring guidelines are good methods of effectively implementing this performance); on this case, the amount of cash you may extract from somebody will probably be quadratically proportional to the extent of personal info that you’ve got, and performing massive quantities of griefing is in the long term assured to value the attacker cash, and never simply threat.
The second is that if customers are identified to be utilizing a number of explicit sources of knowledge, notably on extra subjective questions like “vote on the value of token A / token B” and never simply binary occasions, then these customers will probably be exploitable; for instance, if you realize that some customers have a historical past of listening to Bitstamp and a few to Bitfinex to get their vote info, then as quickly as you get the newest feeds from each exchanges you may probabilistically extract some amount of cash from a participant primarily based in your estimation of which change they’re listening to. Therefore, it stays a analysis drawback to see precisely how customers would reply in that case.
Be aware that such occasions are a sophisticated challenge in any case; failure modes corresponding to everybody centralizing on one explicit change are very more likely to come up even in easy Sztorcian schemes with out this type of probabilistic griefing. Maybe a multi-layered scheme with a second-layer “appeals courtroom” of voting on the high that’s invoked so not often that the centralization results by no means find yourself happening might mitigate the issue, but it surely stays a extremely empirical query.


тирзепатид цена инструкция +по применению +для женщин – mounjaro инструкция +на русском купить, mounjaro тирзепатид